Keywords: CommBox EdgeOS, Traffic Policy
Overview
This guide explains common use cases and scenarios for applying Traffic Policies on an CommBox EdgeOS device. It describes how traffic policies can be used to prioritize, shape, or restrict network traffic for services like VoIP, streaming, gaming, social media, and web browsing. The guide also outlines practical examples of configuring policy rules to control bandwidth, block unwanted applications, or exempt critical services from restrictions. By following this guide, you will understand when and how to apply traffic policies effectively to meet business and network performance goals.
1 What are Traffic Policies
Traffic Policies allow the user to control the upload and download speed for networks and hosts connected to the Edge appliance. Users can also control how much data can be uploaded or downloaded (Quota) on different WAN technologies and how often the data cap or quota is refreshed (0 - 24 hours) by setting Traffic Policies.
Within a Traffic Policy, users can also define an Application Policy Profile. These policies control what applications are allowed and denied. There are over 500 different applications, covering Advertisements and Streaming Media to Software Updates and VPN Software. Each Application Rule can be configured to control the application’s upload and download speed. Traffic policies can be applied at a network or device level using the mac address or IP Address.
1.1 Best Practices for Traffic Policies
When deploying the Edge appliance, the user must consider several things while configuring Traffic Policies.
-
Are there any high-priority users such as the Owner or Guests?
-
Are there any high-cost links that should be controlled?
-
What user experience should the network deliver?
Traffic Policies and Application Policies can become overwhelming if the user attempts to cover every use case immediately. It is better to start small and gradually add on. One way to do this is to define a policy for high-priority users like the Owner or Guest networks. This will ensure that these users have the experience that they expect. Next, define a policy that prevents low-priority users from impeding network traffic for high-priority users. Finally, ensure that all policies control the cost of high-cost links like Fleet Broadband.
Within CommBox EdgeOS there are mechanisms to help the user configure different Traffic Policies. You can duplicate an existing policy (copy icon in the policy list) and use it as a starting point. Once the user has tweaked the policy for one WAN technology, they can use the Copy To option to copy the settings over to the other WAN types (for example Cellular, Ethernet, Starlink and Bonded). Finally, when defining an Application Rule by Domain or IP/Port, use the CSV upload feature if there is a need to add many different rules.
2 Configuring Traffic Policies
-
Log in to the CommBox EdgeOS portal (directly or through the Konnect application).
-
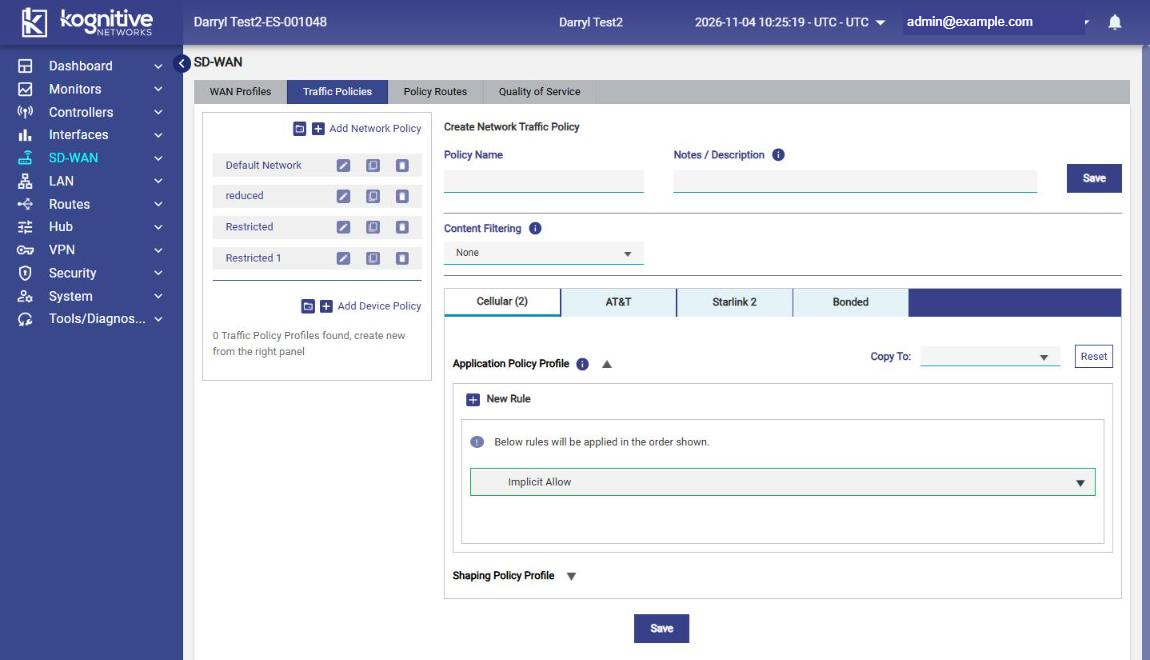
Select SD-WAN > Traffic Policies. Existing policies are listed on the left: network policies at the top and device policies below.
-
Click Add Network Policy to create a policy for an access network (or Add Device Policy for specific devices). Use the pencil icon to edit an existing policy, the copy icon to duplicate it and the delete icon to remove it.
-
Enter the Policy Name and optional Notes / Description.
-
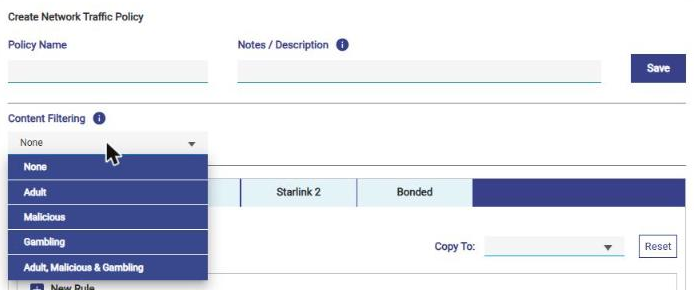
In Content Filtering, select None, Adult, Malicious, Gambling or Adult, Malicious & Gambling.
-
The tabs below (for example Cellular, AT&T, Starlink, Bonded) are the WAN interfaces of the device. Rules are set per WAN tab; use Copy To to copy them to other tabs and Reset to clear them.
-
Click Save when done.
2.1 Shaping Policy Profile
-
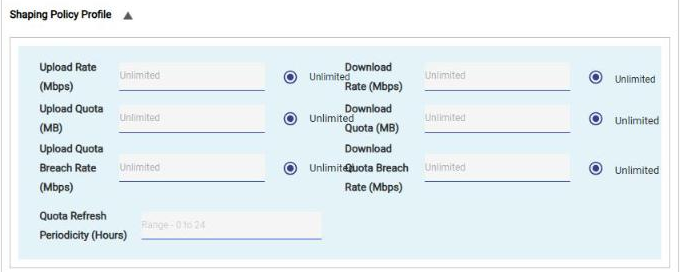
Upload Rate and Download Rate (Mbps) - speed limits for the network.
-
Upload Quota and Download Quota (MB) - data allowed per refresh period.
-
Upload Quota Breach Rate and Download Quota Breach Rate (Mbps) - speed after the quota is used up (0 blocks traffic).
-
Quota Refresh Periodicity (Hours) - 0 to 24 hours; how often the quota is reset.
-
Each value has an Unlimited option; clear it to enter a value.
2.2 Application Policy Profile
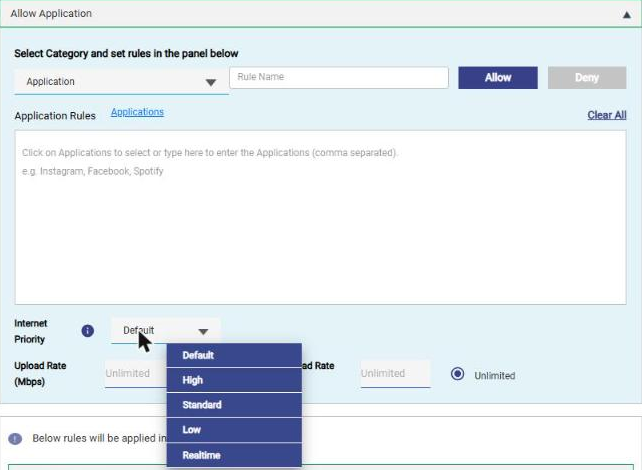
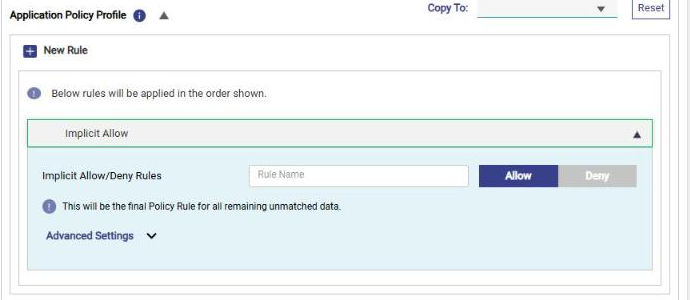
Rules are applied in the order shown. To add one, click New Rule under Application Policy Profile, choose the Select Category, enter a Rule Name and click Allow or Deny. Each rule can also set an Internet Priority (Default, High, Standard, Low, Realtime) and its own Upload Rate / Download Rate. The final Implicit Allow rule handles all unmatched traffic; expand it and click Deny to block everything not allowed by the rules above.
2.2.1 Domain based rules
-
Set Select Category to Domain.
-
Enter the domains in
*.<domain name>format, separated by commas. If Captive Portal is enabled and HTTP Redirect is disabled, add*.k4mobility.com, *.cloudflareinsight.com. -
To add many domains, download the template from the CSV link, fill it in and upload it with the folder icon.
2.2.2 Application based rules
-
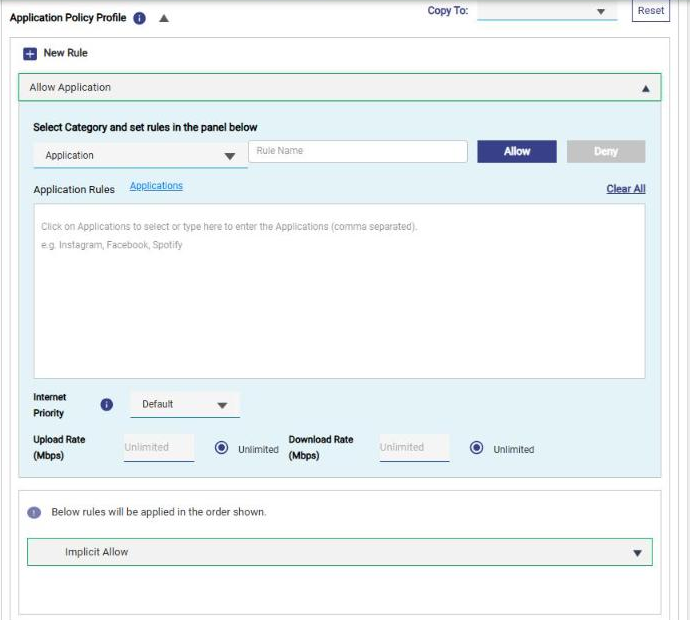
Set Select Category to Application.
-
Click Applications and select applications or whole categories (for example All Social Media), or type application names separated by commas.
2.2.3 IP & Port based rules
-
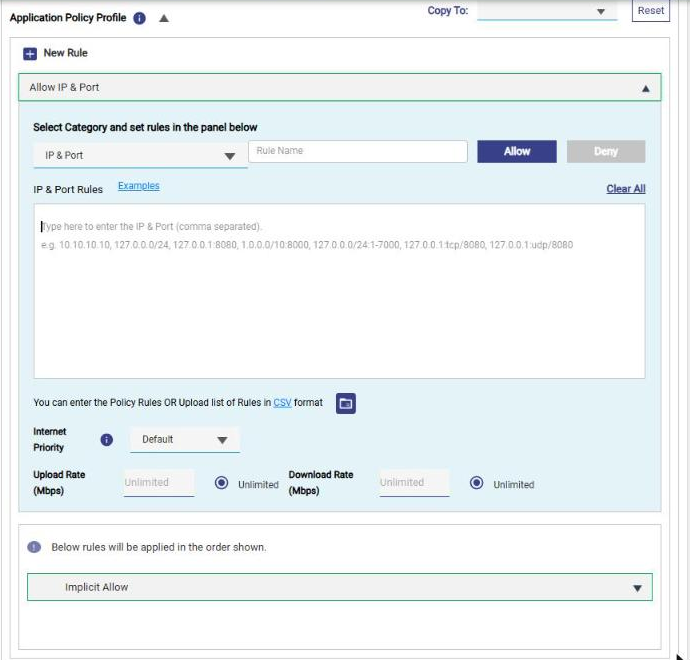
Set Select Category to IP & Port.
-
Enter IP and port combinations separated by commas. The protocol can be included, for example
10.10.10.10,127.0.0.0/24,1.0.0.0/10:8000,127.0.0.1:tcp/8080or127.0.0.1:udp/8080. Click Examples for more formats. -
Use the CSV template and folder icon to upload many entries.
2.2.4 Protocol based rules
-
Set Select Category to Protocol and select the protocols the rule applies to.
3 Use Cases
Some of the most common use cases are shown below.
3.1 Deny access to all Social Media and Streaming applications
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
Click New Rule under Application Policy Profile. Keep the category as Application.
-
Click Applications and select All Social Media and All Streaming Media.
-
Click Deny.
-
Click Save. Users on this network can no longer use social media or streaming applications.
3.2 Allow access only to a known set of IPs, domains and applications
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
Add an IP & Port rule with the allowed IPs (for example
10.10.10.10) and click Allow. -
Add a Domain rule with the allowed domains (for example
*.abc.com) and click Allow. -
Add an Application rule with the allowed applications (for example Instagram, Facebook) and click Allow.
-
Expand the final Implicit Allow rule and click Deny.
-
Click Save. Only the listed IPs, domains and applications are reachable.
3.3 Set a maximum daily quota for crew
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
Expand Shaping Policy Profile.
-
Set Upload Quota and Download Quota (for example 1000 MB each).
-
Set Upload Quota Breach Rate and Download Quota Breach Rate to 0 so users have no internet after the quota is used.
-
Set Quota Refresh Periodicity to 24 hours.
-
Click Save. Users cannot exceed the daily quota.
3.4 Deny access to adult and malicious content
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
In Content Filtering, select Adult, Malicious or Gambling, or Adult, Malicious & Gambling to block all three.
-
Click Save. Access to the selected categories of content and to malicious, blacklisted domains is blocked.
3.5 Set bandwidth for a particular application
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
Click New Rule under Application Policy Profile. Keep the category as Application and select the application.
-
Set the Upload Rate and Download Rate (Mbps) for the application.
-
Click Allow.
-
Click Save.
3.6 Effective VoIP and WhatsApp calling
-
Open or create the policy in SD-WAN > Traffic Policies and select the WAN tab.
-
Click New Rule under Application Policy Profile. Keep the category as Application.
-
Select All VoIP/Conferencing and WhatsApp.
-
Set Internet Priority to Realtime and click Allow.
-
Click Save. Voice and video calls get the highest priority.