
Keywords: CommBox EdgeOS, VPN, Wireguard VPN, IPSec VPN
Overview
This guide explains how to configure VPN (Virtual Private Network) services on an CommBox EdgeOS device to securely connect remote sites and centralized networks. It covers common VPN use cases and step-by-step setup for both Wireguard VPN and IPSec VPN, including creating VPN endpoints, generating and applying client profiles, and associating access networks with VPN tunnels. By following this guide, you will be able to establish secure encrypted connections between CommBox EdgeOS devices, enabling remote site connectivity and controlled routing of network traffic through VPN tunnels.
1 VPN - Use Cases
CommBox EdgeOS VPN services are useful for connecting Remote to Centralized Sites/Systems. For example, connecting remote CommBox EdgeOS sites to a more centralized office with CommBox EdgeOS system that is hosting corporate services (VOIP, File Services). The CommBox EdgeOS supports this via Wireguard VPN endpoints, and some use cases are discussed here.
In CommBox EdgeOS 8.x, VPN connections can use a WAN profile. Ideally choose a priority-based WAN profile (SD-WAN > WAN Profiles, with WANs set at Highest Priority, Priority 2, and so on) rather than a bonding profile. The KVH VPN uses one WAN link at a time; if the active link fails, the VPN moves to the next WAN in priority order.
1.1 Use Case 1 - Single Remote Site using Multiple Hub-Side VPN EdgeServers
It is common for remote sites to require point to point VPN connections to various centralized sites. A common example would be a EdgeServer at a remote site that requires:
-
Local Internet access,
-
Local Media System requires Internet access from a specific home location, &
-
Local Management Network requires connectivity to an Operations Centre.
A visual for this is provided here:
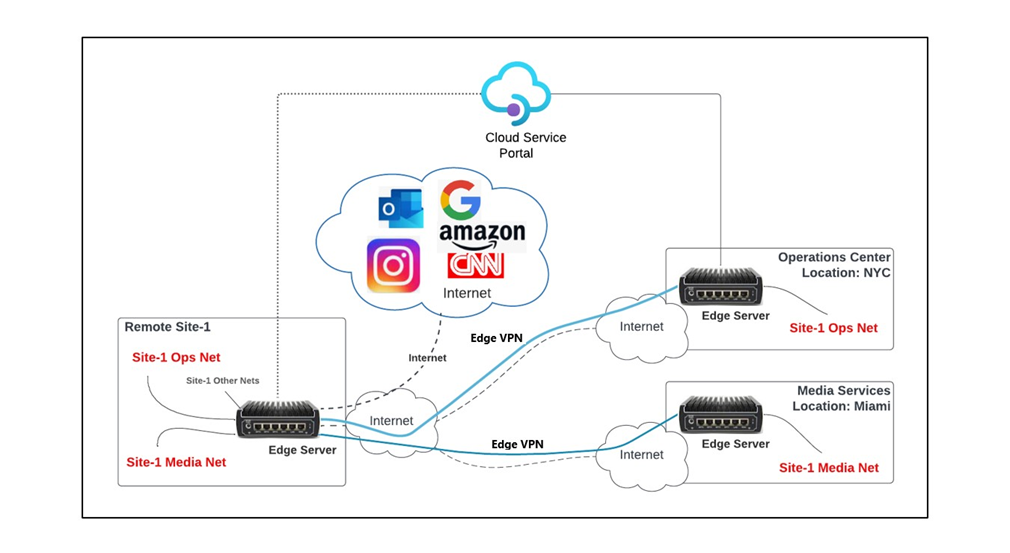
The VPN User Guide will define the steps to build a VPN from remotes sites to centralized centers. CommBox EdgeOS Enterprise VPN supports:
-
Site - 1 can select an Access Networks to utilize a specific VPN instance Configured.
-
Above Example: all of the Site-1 Ops Net Access Network will utilize VPN to the Operations Centre.
-
-
VPN will utilize the WAN profile configured for that Access Network, including transport over PEP/Advanced Bonded WAN interfaces.
-
Access Networks using VPN will egress the Centralized VPN server natively – NO NAT.
-
Access Networks not selected to use VPN will egress via the defined WAN Profile rulesets.
1.2 Use Case 2 - Multiple Remote Sites Using a Common Hub-Side VPN EdgeServer
It is common for multiple remote sites to VPN to a common centralized site or Hub. A common example would be an EdgeServer at a remote site that requires:
-
Local Internet access,
-
Remote Media System requires Internet access from a Hub-side location, &
-
Remote Management Network requires connectivity to a Hub-side Operations Centre.
A visual for this is provided here:
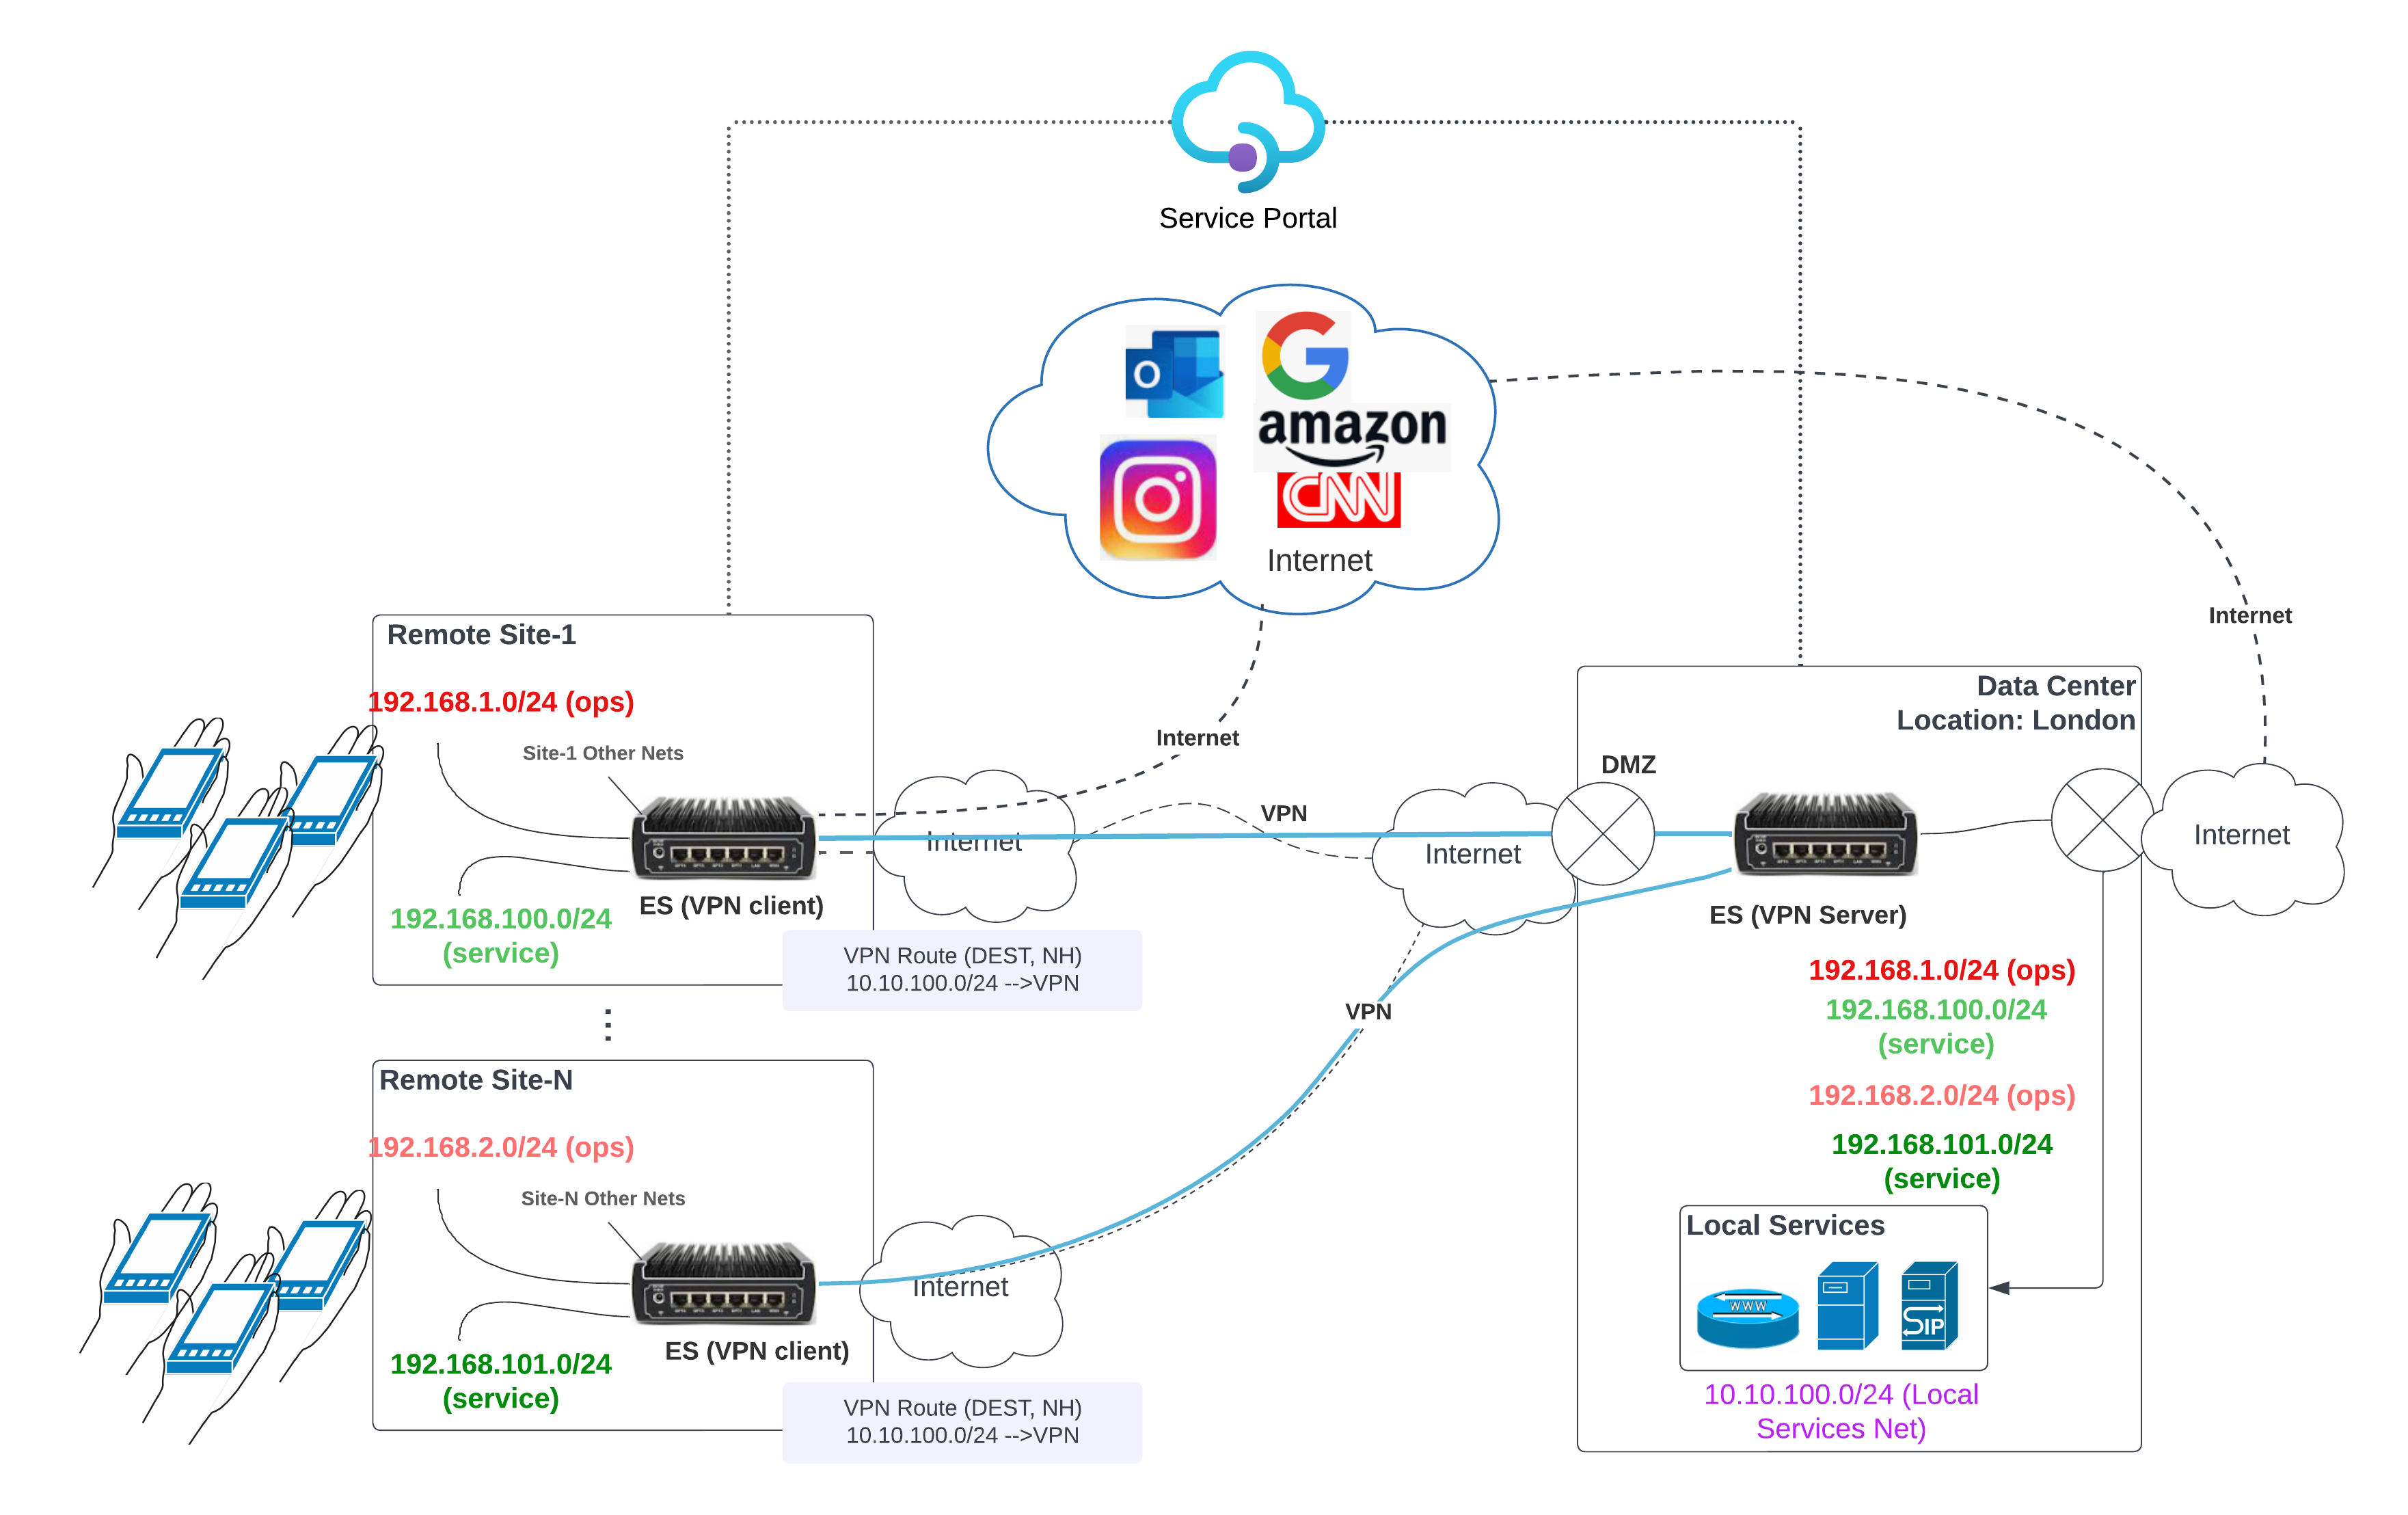
The VPN User Guide will define the steps to build a VPN from remotes sites to centralized centers. CommBox EdgeOS Enterprise VPN supports:
-
Hub-Side EdgeServer VPN Server “configures” VPN Server.
-
Public Listening IP/Port (from DMZ).
-
Configures a VPN Client profile for each remote EdgeServer.
-
Load Specific VPN Client profile on target remote EdgeServer.
-
-
Each remote EdgeServer can select/create Access Network to utilize a specific VPN profile loaded.
-
As well Set Destination Routes that will use the VPN profile (can be all, or targeted Networks) – split tunnel.
-
-
Now, Access Networks (and target routes) will use VPN, and this will traverse the WAN link defined by the WAN profile configured for that Access Network, including transport over PEP/Advanced Bonded WAN interfaces.
-
Access Networks using VPN will egress the Centralized VPN server natively – NO NAT.
-
Access Networks not selected to use VPN, or destination networks not routing over VPN will egress via the defined WAN Profile rulesets.
2 Wireguard VPN
The Wireguard VPN feature creates VPN tunnels between CommBox EdgeOS devices, with one device acting as the VPN Server (for example the Operations Center) and others as VPN Clients (remote sites).
-
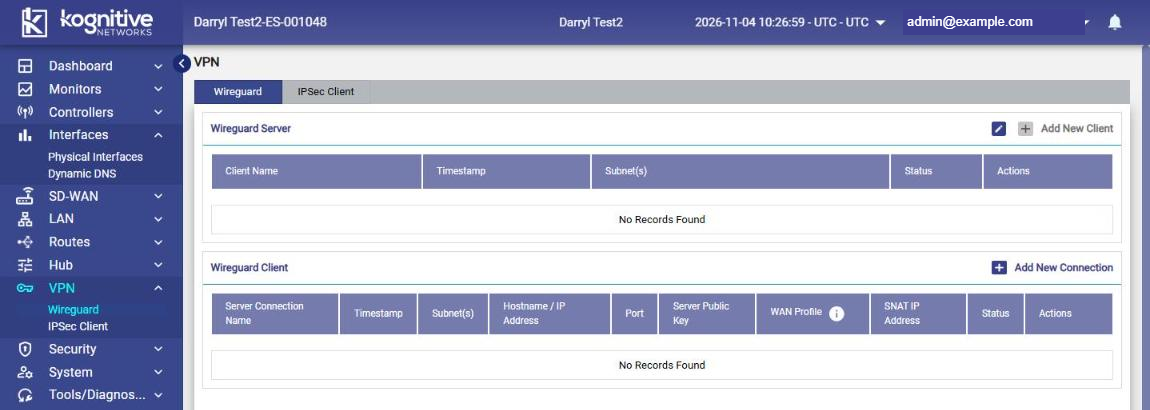
Log in to the CommBox EdgeOS portal.
-
Select VPN > Wireguard. The page has two sections: Wireguard Server (Client Name, Timestamp, Subnet(s), Status, Actions) and Wireguard Client (Server Connection Name, Timestamp, Subnet(s), Hostname / IP Address, Port, Server Public Key, WAN Profile, SNAT IP Address, Status, Actions).
2.1 Configure the Wireguard VPN Server
A Wireguard VPN Server listens on an IP address (or FQDN) and UDP port that the VPN clients can reach; in most cases this must be a reachable public IP.
-
On the server device, go to VPN > Wireguard and click the pencil icon in the Wireguard Server section. The Wireguard Server Settings dialog opens.
-
Enter the Hostname / IP Address (for example myoffice.com) and the Port (for example 2022).
-
Click Save. The server is now listening on that IP:port.
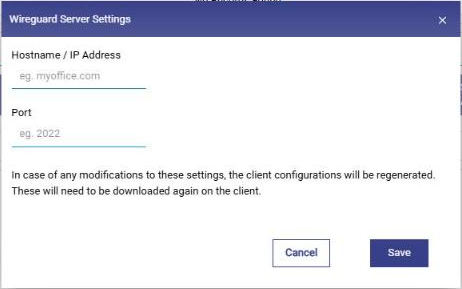
If you change these settings later, the client configurations are regenerated and must be downloaded and loaded on the clients again.
Caution: avoid using a Virtual IP for the WAN interface of the device acting as Wireguard server. A Starlink Virtual IP (VIP) interface might block inbound connections and cause inbound requests to fail.
2.2 Create a Wireguard VPN Client Profile on the VPN Server
-
In the Wireguard Server section, click Add New Client. (The button is enabled once the server settings are saved.)
-
Set a unique Client Alias Name; it is for local reference only.
-
Set the subnet(s) that will be routed through the VPN tunnel from the client. This sets the IP routes on the server to forward these IPs back through the tunnel to the remote client.
-
Save the client profile. The new client is listed in the Wireguard Server section.
Make sure a route is entered (for example 10.0.0.0/24), not a host IP (for example 10.0.0.1/24). A subnet that overlaps with another client profile, or with IP space on the server device, causes routing conflicts.
2.3 Download the Client Profile
Download the client profile with the download icon in the Actions column of the client. The file is named after the client alias with a .json extension (for example test.json). A client profile must be created for every VPN client connecting to the server.
2.3.1 Delete a Client Connection
To delete a client connection, click the delete icon in its Actions column. A client connection cannot be edited; delete it and create it again.
2.4 Configure the Wireguard VPN Client
A device can have multiple Wireguard client connections, for example one tunnel per access network. The connections can end on the same VPN server or on different servers. Each client connection is configured with a client profile downloaded from a Wireguard VPN server.
-
Log in to the remote (client) device and select VPN > Wireguard.
-
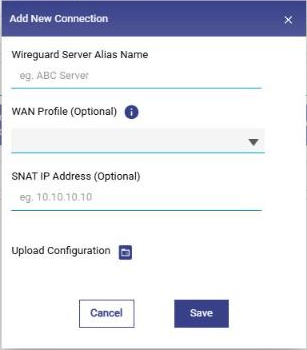
In the Wireguard Client section, click Add New Connection. The Add New Connection dialog opens.
-
Enter a unique Wireguard Server Alias Name (local reference only).
-
Optionally select the WAN Profile the VPN should use when leaving the local device (priority-based recommended).
-
Optionally enter a SNAT IP Address (for example 10.10.10.10).
-
Click the Upload Configuration folder icon and select the client profile (.json) downloaded from the server.
-
Click Save.
2.4.1 Edit or Delete a Server Connection
Use the icons in the Actions column of the connection. Edit (pencil) lets you change the connection name and WAN profile; confirm with the green tick. Delete asks for confirmation.
The VPN between the client and server is now set up. Next, associate an access network on the client device with the VPN (section 4).
3 IPSec VPN
The IPSec VPN feature creates VPN tunnels between an CommBox EdgeOS device acting as IPSec VPN client (remote site) and an IPSec VPN server (for example an Operations Center). A device can have multiple IPSec client connections, for example one tunnel per access network.
3.1 Add an IPSec VPN Server Connection
-
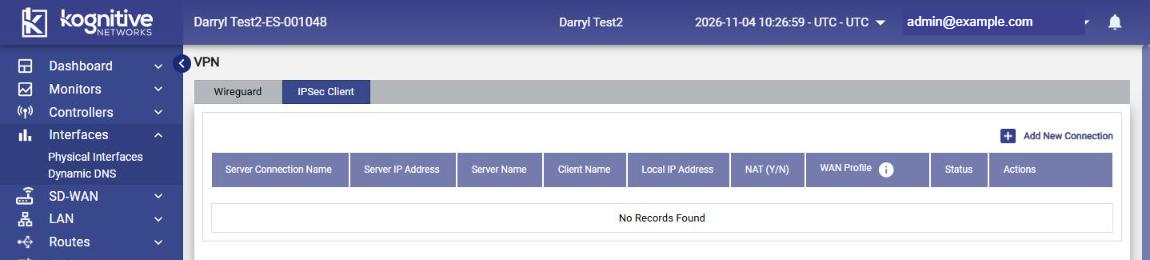
Log in to the remote (client) device and select VPN > IPSec Client. The table lists Server Connection Name, Server IP Address, Server Name, Client Name, Local IP Address, NAT (Y/N), WAN Profile, Status and Actions.
-
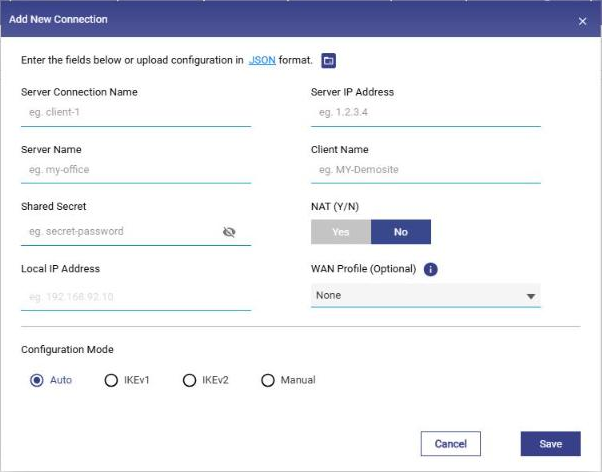
Click Add New Connection. The Add New Connection dialog opens.
-
Server Connection Name - the name used for this connection; it must be unique across all VPN connections (IPSec and Wireguard).
-
Server IP Address - the IP of the IPSec server. Unlike Wireguard, only one IPSec connection is allowed per server IP.
-
Server Name and Client Name - identifiers used by the server and this client to authenticate each other.
-
Shared Secret - the password shared between server and client (use the eye icon to show it).
-
NAT (Y/N) - select Yes if the client is assigned a single IP address and enter it in Local IP Address; select No otherwise (Local IP Address is then disabled).
-
WAN Profile (Optional) - the WAN profile for this connection.
-
Configuration Mode:
-
Auto (default) - the client negotiates the security algorithms with the server using IKEv2.
-
IKEv1 - choose whether the server uses Aggressive mode (Yes/No), then select the IKE (Phase 1) and ESP (Phase 2) algorithms. The PRF list includes a None option.
-
IKEv2 - as IKEv1, without the Aggressive/Main mode choice.
-
Manual - upload a configuration snippet in StrongSwan ipsec.conf format (name = value entries). Download the sample file, fill it in and upload it with the folder icon.
-
-
Instead of filling in the fields, you can click the JSON link to download a sample file, fill it in, and upload it with the folder icon next to it; the fields are filled from the file.
-
Click Save.
3.1.1 Edit or Delete a Server Connection
Use the pencil (edit) or delete icon in the Actions column. Delete asks for confirmation.
4 Assign Access Networks (VLAN) to the VPN
On the remote (client) device, associate one or more access networks (VLANs) with the VPN. All traffic from that access network then flows through the VPN tunnel to the server specified in the client profile.
-
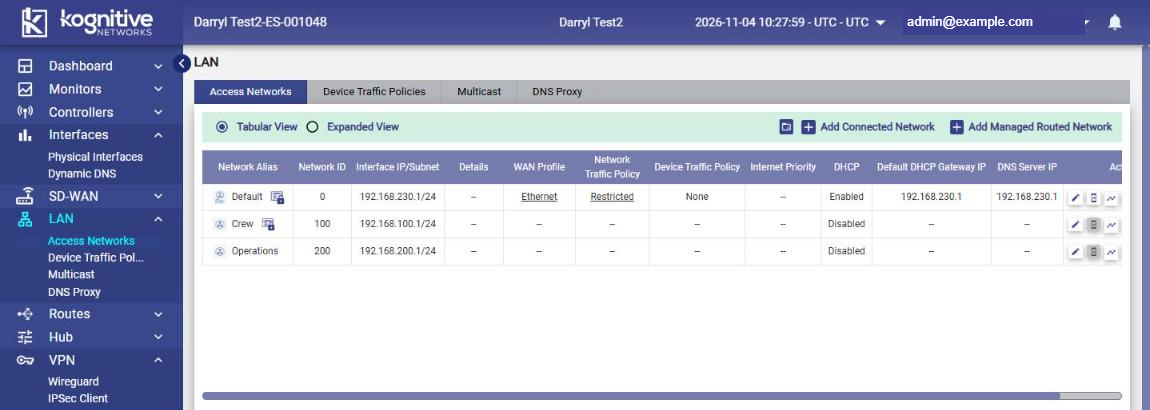
Log in to the client device and select LAN > Access Networks.
-
Click the pencil icon of the access network that should use the VPN. (You can also set this when creating a network with Add Connected Network.)
-
In the network form, go to the VPN section. It is available once at least one VPN connection is configured on the device.
-
Click + Tunnel to associate a route with a VPN connection. Route 0.0.0.0/0 is the default route. You can define several routes (split tunnel); any route not in this table uses the normal routing of the device and its WAN profile.
-
Select the VPN connection in Server Connection Name, enter the Routes in CIDR format and click the green tick (X cancels).
-
Save the access network.
Make sure the subnet of the access network matches the subnet specification of the server connection (routing). If the VPN goes down, the access network using it is down as well. With a priority WAN profile (for example Ethernet priority 1, Cellular priority 2) the VPN moves to Cellular if Ethernet fails, so the network keeps internet access. With a single WAN, or if the VPN cannot be established, the network is down.
5 VPN status on the Dashboard
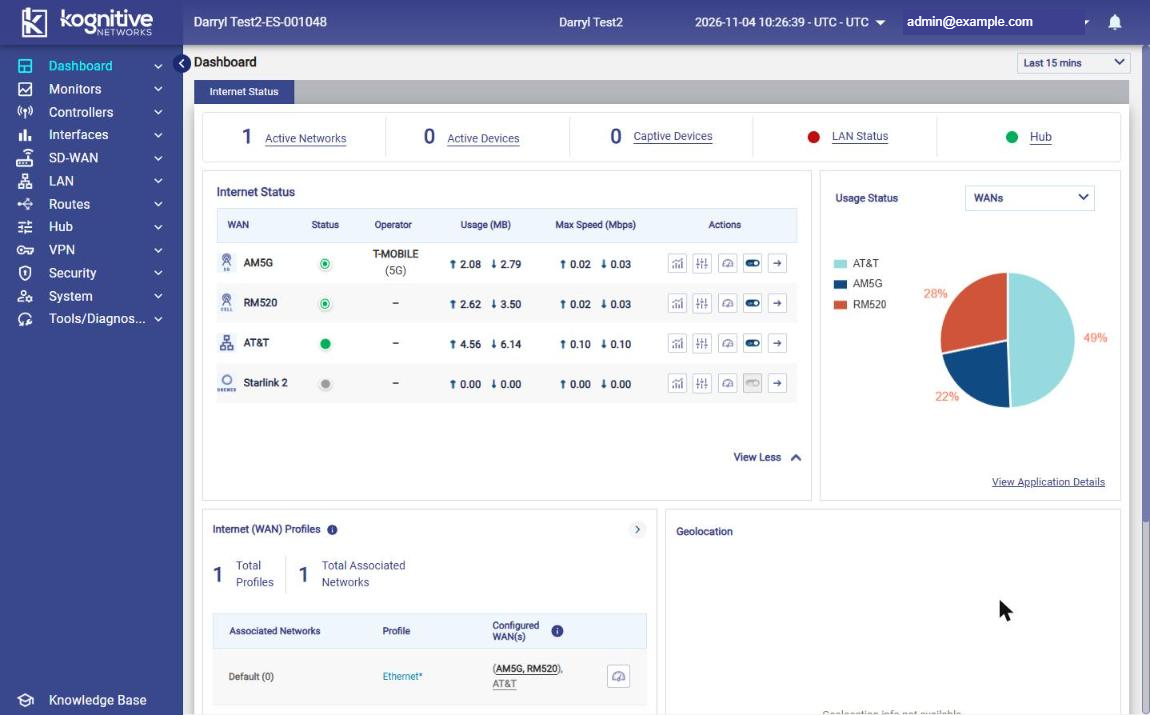
An overview of the VPN status is shown on Dashboard > Internet Status. A VPN Server section appears when at least one client connection is configured, and a VPN Client section appears when at least one server connection is configured. Hover over the icon to the left of a connection name in the VPN Client section to see whether it is Wireguard or IPSec. If no VPN is configured, no VPN section is shown (as in the example below).
6 Firewall Settings
Once the VPN tunnels are up, you can use firewall rules to stop remote access networks from reaching each other and/or the server-side access networks.
6.1 Blocking Remote Networks from Each Other
For example, using Use Case 2 above, set a rule on the VPN server device to block traffic between Remote Site-1 access network 192.168.1.0/24 and Remote Site-2 access network 192.168.2.0/24:
-
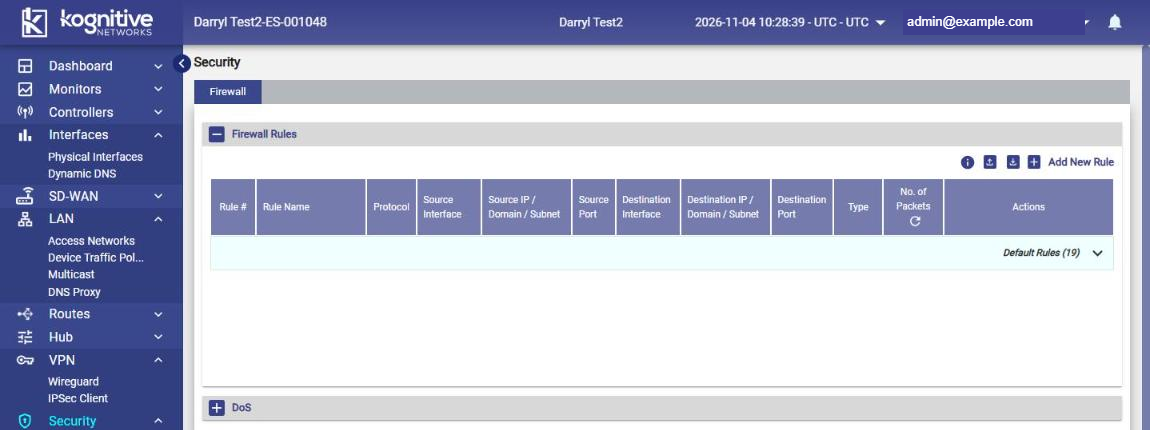
On the VPN server device, select Security > Firewall.
-
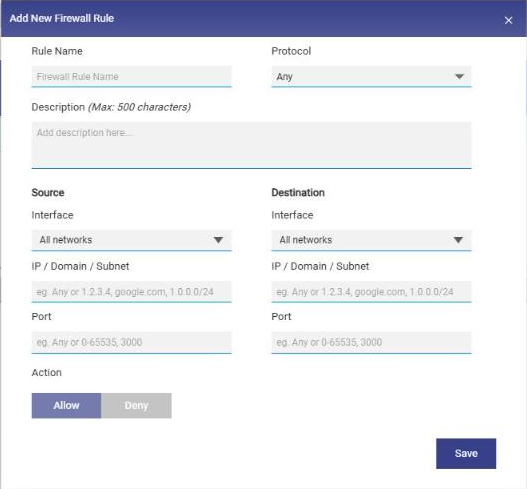
Click Add New Rule. The Add New Firewall Rule dialog opens.
-
Enter a Rule Name and optional Description. Leave Protocol as Any (or select a protocol to be more specific).
-
Under Source, leave Interface as All networks and enter the remote network in IP / Domain / Subnet (192.168.1.0/24). Leave Port empty (Any).
-
Under Destination, leave Interface as All networks and enter the other remote network (192.168.2.0/24).
-
Set Action to Deny and click Save.
-
The rule appears in the Firewall Rules table (Rule #, Rule Name, Protocol, Source Interface, Source IP / Domain / Subnet, Source Port, Destination Interface, Destination IP / Domain / Subnet, Destination Port, Type, No. of Packets, Actions). Use the Actions buttons to change the order or add a mirror (reverse) rule.
-
You can narrow the rule to a single host or add protocol/port details if needed.
-
To block remote networks from reaching the local networks of the VPN server, set the same kind of rule on the remote site device.
Appendix: Wireguard VPN Client Usage with EdgeServer Wireguard VPN Server
Another consideration to leverage the Wireguard VPN services, would be to setup a VPN Client on one’s Laptop (windows, macos) or mobile (android, ios). The VPN Client is “Wireguard” and is available at: Installation - WireGuard. The EdgeServer Wireguard VPN Server configuration is no different for this option, thus follow those steps. The Laptop VPN Client configuration is outlined here for windows:
-
Install the Wireguard for Windows.
-
Note that the EdgeServer Wireguard VPN Server will not assign an IP address’ or set routes for the Wireguard VPN client at this time.
-
What the Wireguard VPN client can provide, is a simple way to validate the End2End VPN configuration, and Internet reachability.
-
-
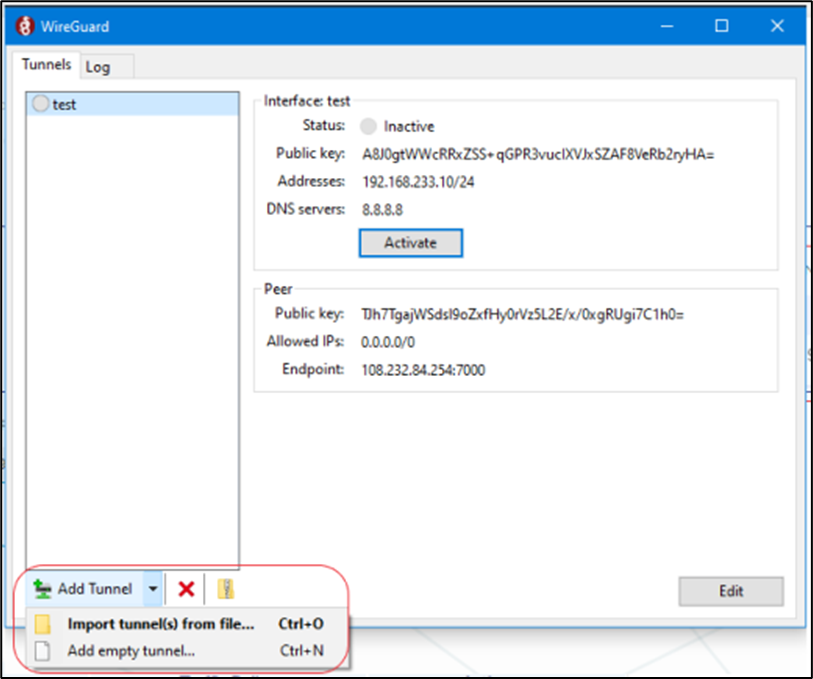
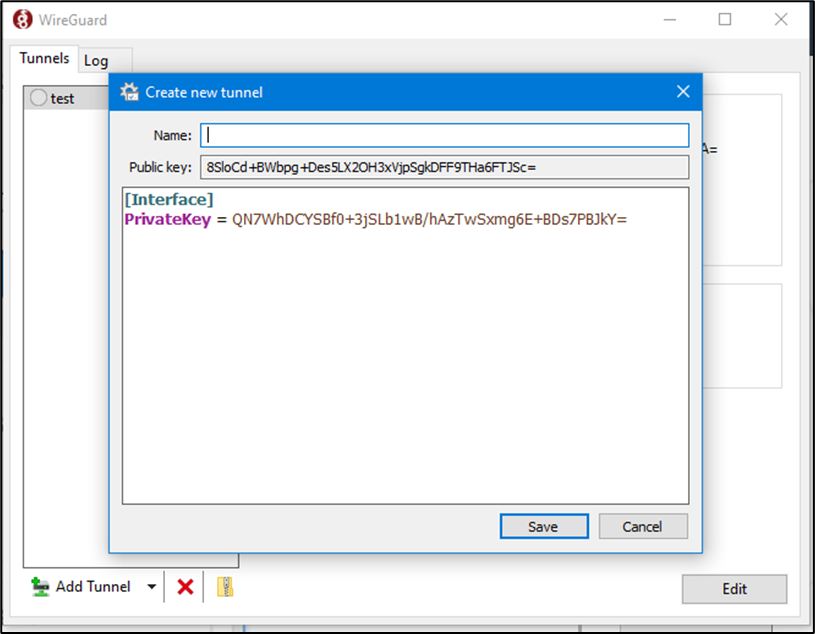
Click on ‘Add Tunnel’ Lower left, select ‘Add empty tunnel’.
-
This provides a dialogue to configure the Wireguard VPN Client.
-
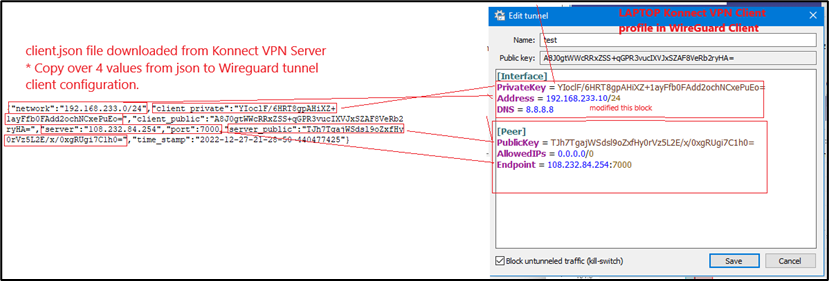
Note that the following fields will need to be added:
-
At Top:
-
Name – set a local “alias name” for the VPN profile – likely the EdgeServer connecting too.
-
PublicKey -> Cannot change this.
-
-
In Working Space:
-
[Interface] – Wireguard VPN Client configuration
-
PrivateKey -> Utilize client_private Key value from client.json file
-
Address -> Utilize network value from the client.json – this was defined on the EdgeServer Wireguard VPN server.
-
DNS -> DNS server – optional.
-
-
[Peer] – Wireguard VPN Server configuration
-
PublicKey -> Utilize server_public key from client.json file
-
AllowedIPs -> Set to 0.0.0.0/0 to allow all IP.
-
Endpoint -> Set to public IP (name) and listening port of Wireguard VPN Server – this is within client.json file.
-
-
When done – click Save, and the final tunnel file will look similar to:
-
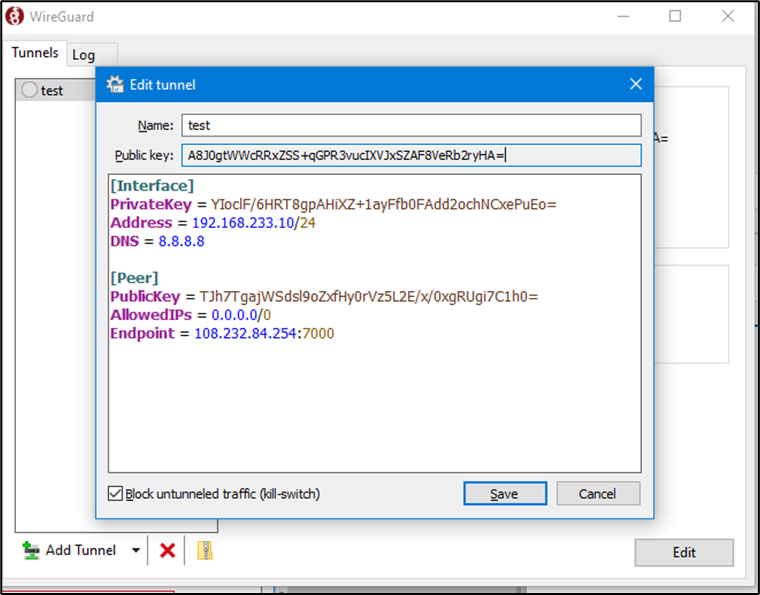
Now, to test the connection simply highlight the client profile created in the Wireguard VPN Client, “test” here, and click “Activate”. It will state “Active” if connected or NOT. Thus to test if internet is available, open a browser to verify if the Internet is available. If yes, one can verify the internet IP by doing a whatismyip check.